WHO WE ARE
We are a team of cybersecurity experts passionate about protecting businesses from evolving digital threats. With over a decade of proven experience, we deliver security that’s proactive, not reactive — built around your business, not a one-size-fits-all playbook.
- Certified Experts
- Proven Methodologies
- Customer First Approach
- IDENTITY VERIFIED // FOUNDER DOSSIER
CLEARANCE: LEVEL-01 CHIEF ARCHITEC
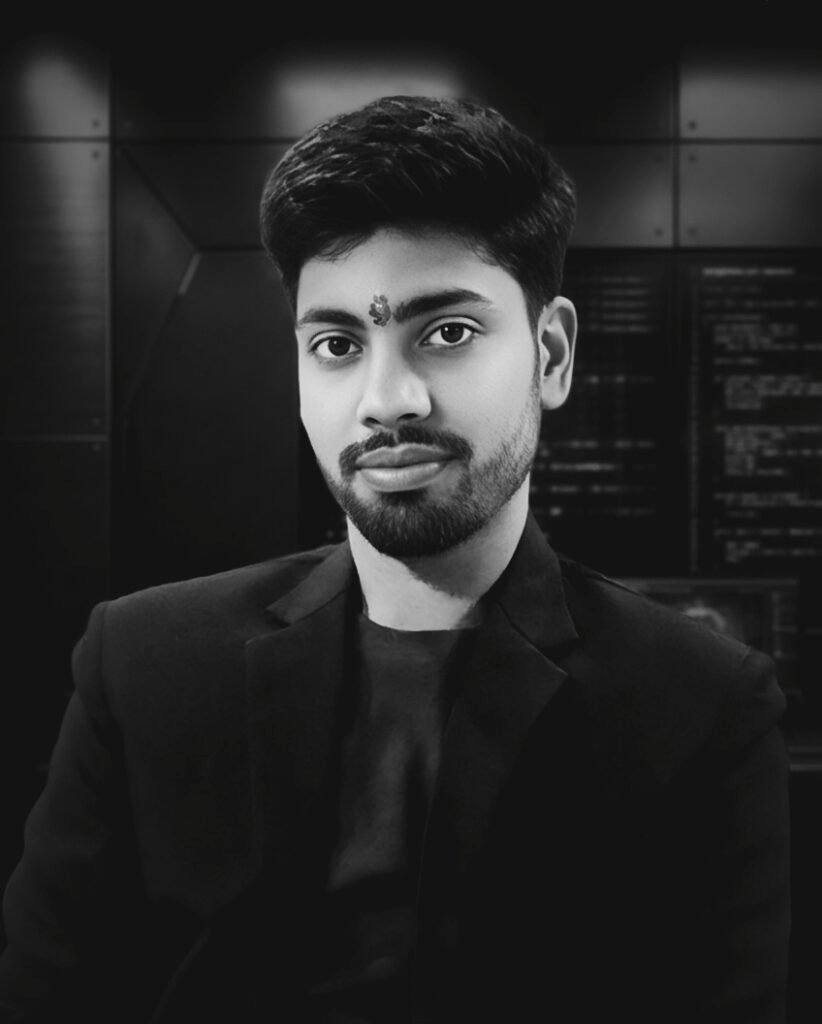
Saurabh Pandey
FOUNDER & SECURITY ARCHITECT
CORE FOCUS
Offensive Defense & Web Tech
METHODOLOGY
Offensive Defense & Web Tech
SECURITY OPS
Vulnerability Research
ORIGINS // 01
Systems Break Where Assumptions Begin
My work started in quantitative analysis and systems logic. When evaluating complex networks, numbers and logs never lie. Approaching technology with an analytical mindset makes one thing obvious: security incidents and traffic drops aren’t bad luck—they are the direct consequence of neglected fundamentals and unverified dependencies.
STRATEGY // 02
Breaking the Silo Between Code and Security
In the tech industry, developers write features without understanding offensive attack paths, while digital marketers build campaigns on fragile, bloated websites. When a breach happens or a server crashes, third-party contractors point fingers. High-ranking, scalable platforms require cybersecurity defense, clean development, and technical SEO working inside the exact same codebase.
DIRECTIVE // 03
No Shortcuts. Continuous Verification.
ABYNERO was created to deliver technical precision without vanity metrics. Whether auditing application security, configuring server firewalls, or optimizing an enterprise site for search visibility, our standard is measurable: zero critical vulnerabilities, sub-second latency, and digital infrastructure built for the long haul.
OPERATIONAL DIRECTIVE
Engineering Secure Foundations That Compound in Value
We replace surface-level compliance with offensive cybersecurity testing and high-speed web engineering—building platforms that stay fast, rank high, and resist real-world threats.
CORE MISSION
Eradicating Digital Fragility Before It Costs You
Most digital platforms fail because they treat security and development as separate silos. Our mission is to bridge this gap by delivering offensive penetration testing, threat surface reduction, and clean-code development directly into your product lifecycle. We don’t just find vulnerabilities; we help engineering teams fix architectural flaws, achieve sub-second server response times, and establish dependable search engine authority without shortcuts.
STRATEGIC VISION
Security as a Measurable Growth Multiplier
We envision a future where business owners and founders never have to choose between fast growth and robust cyber defense. Security should not slow down innovation or break marketing budgets. By combining automated telemetry, manual vulnerability research, and hardened infrastructure standards, our vision is to make resilient cybersecurity and technical search visibility the baseline standard for every growing business.
TECHNICAL INTELLIGENCE // FAQ
Frequently Addressed Security and Architecture Queries
Detailed operational insights into our threat assessment methodologies, zero-downtime auditing, and technical infrastructure standards.
How does a manual penetration test differ from automated scanners?
Will security audits cause downtime for our live production systems?
How do security hardening and clean infrastructure impact SEO rankings?
What compliance standards and vulnerability frameworks do you test against?
Do you provide technical support for patching vulnerabilities after an audit?
What Drives Us
Our Core Values
Precision Over Panic
Calm, methodical response beats hurried reaction. We plan for the incident before it happens.
Cyber threats don't take breaks.
Neither Do We.
Partner with us and stay protected, every second, every day.